Security
Security and governance, built in
How Mission Control keeps credentials, agents, and data in check today, with every statement tied to how the product works.
What ships today
The controls, one group at a time.
Everything on this page describes the product as it works today. Planned work is listed separately at the end.
Data and credentials
Sign-in tokens are encrypted on the Mac, secrets can't be read back, and files start private.
- On the Mac, your sign-in session and the tokens the app keeps are encrypted with the macOS Keychain, never stored in plain files.
- Agent secrets are write-only. Once saved, they can be replaced but never read back.
- SuperGloo reaches only the folders on your Mac that you grant, and confirms before it writes, moves, or deletes anything in them.
- New files in the Library start private to you until you share them.
Agent controls
Decide which agents exist, who can see them, and when they stop to ask a person.
- A project agent belongs to one project and is visible only to that project's members.
- A workspace-wide agent can be restricted to an allowlist of members and roles. Nobody else can see or message it.
- Managers can pause, resume, archive, and restore a Public Agent at any time.
- Public Agents stop and ask with a card before they create or change an automation, or when they need access to a project. Members can answer from desktop or phone.
- SuperGloo asks first before it deletes something, sends or posts to other people, or does more than you asked.
- Agents on your Mac run reads in connected tools on their own and ask for approval before writes or unknown actions.
Admin governance
A role for every member, custom roles for how your organization works, and a record of every governance change.
- Every member has a role. Owner, Admin, and Member are built in, and you can create custom roles from a catalog of workspace permissions.
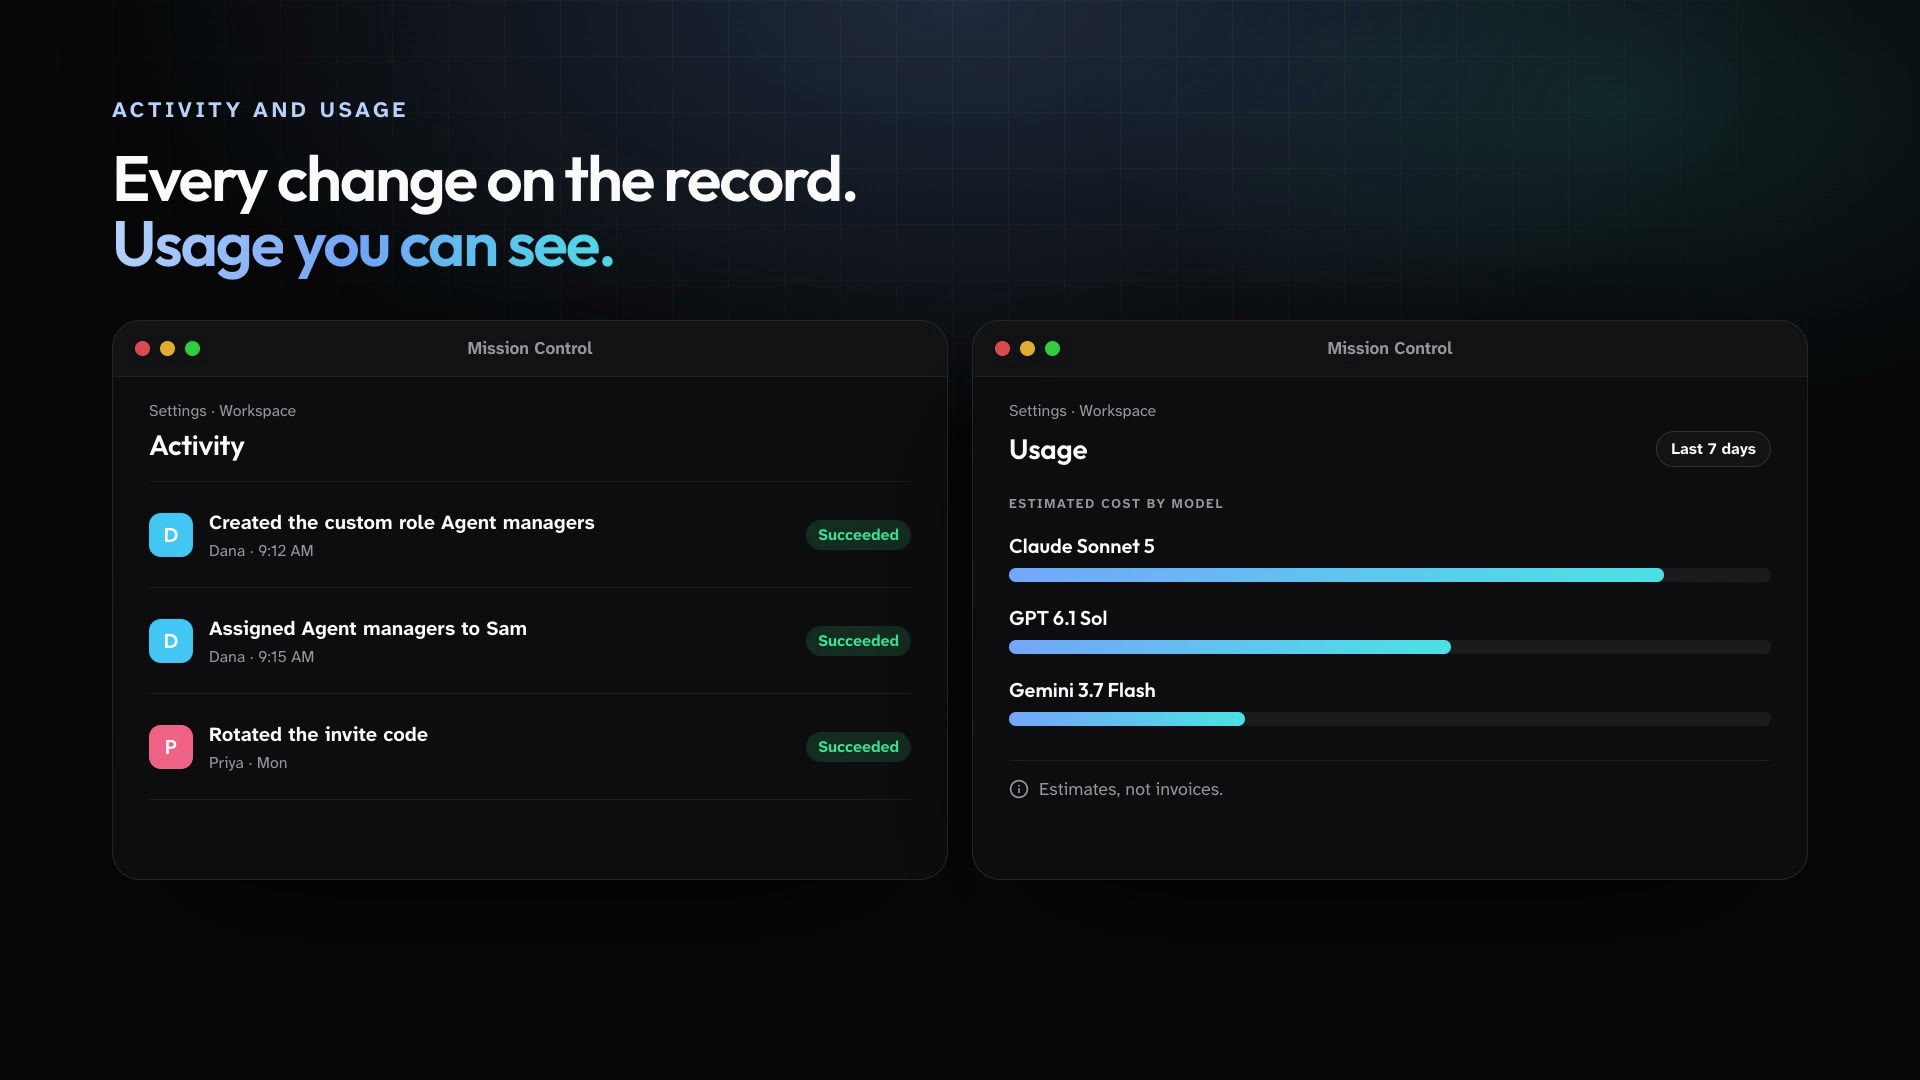
- Governance changes are recorded in an append-only audit log that admins can review.
- Admins add custom MCP servers for the whole workspace and choose which people and agents can use each one.
Models and usage
Models come from a curated catalog through a server-side proxy, and usage is visible to admins as estimates.
- Model provider keys stay on the server. The apps reach models through an authenticated proxy and never hold a provider key.
- Models come from a curated catalog. Nobody pastes provider API keys into the app.
- Usage shows tokens and estimated cost by member, model, and agent. They are estimates, not invoices.
Isolation
Cloud agents run apart from each other and from your devices.
- Each Public Agent and each member's SuperGloo runs in its own cloud sandbox.
- Public Agents run in the cloud, so they keep working when every laptop is closed.
On the roadmap
Single sign-on
Planned work, kept apart from what ships today so you can plan around it honestly.
- Single sign-on through WorkOS.
Not available today. Planned work, not a commitment to a date.
Questions about security?
Ask in the Mission Control community on Discord. There is no contact form, and that's where the people who build it answer.